Focused Compose review
Surfaces privileged mode, host networking, unpinned images, public ports, writable host binds and absent health checks.
Day 041 / DevOps / Docker
A dependency-free Python CLI that performs a focused, read-only audit of normalized Docker Compose configuration.
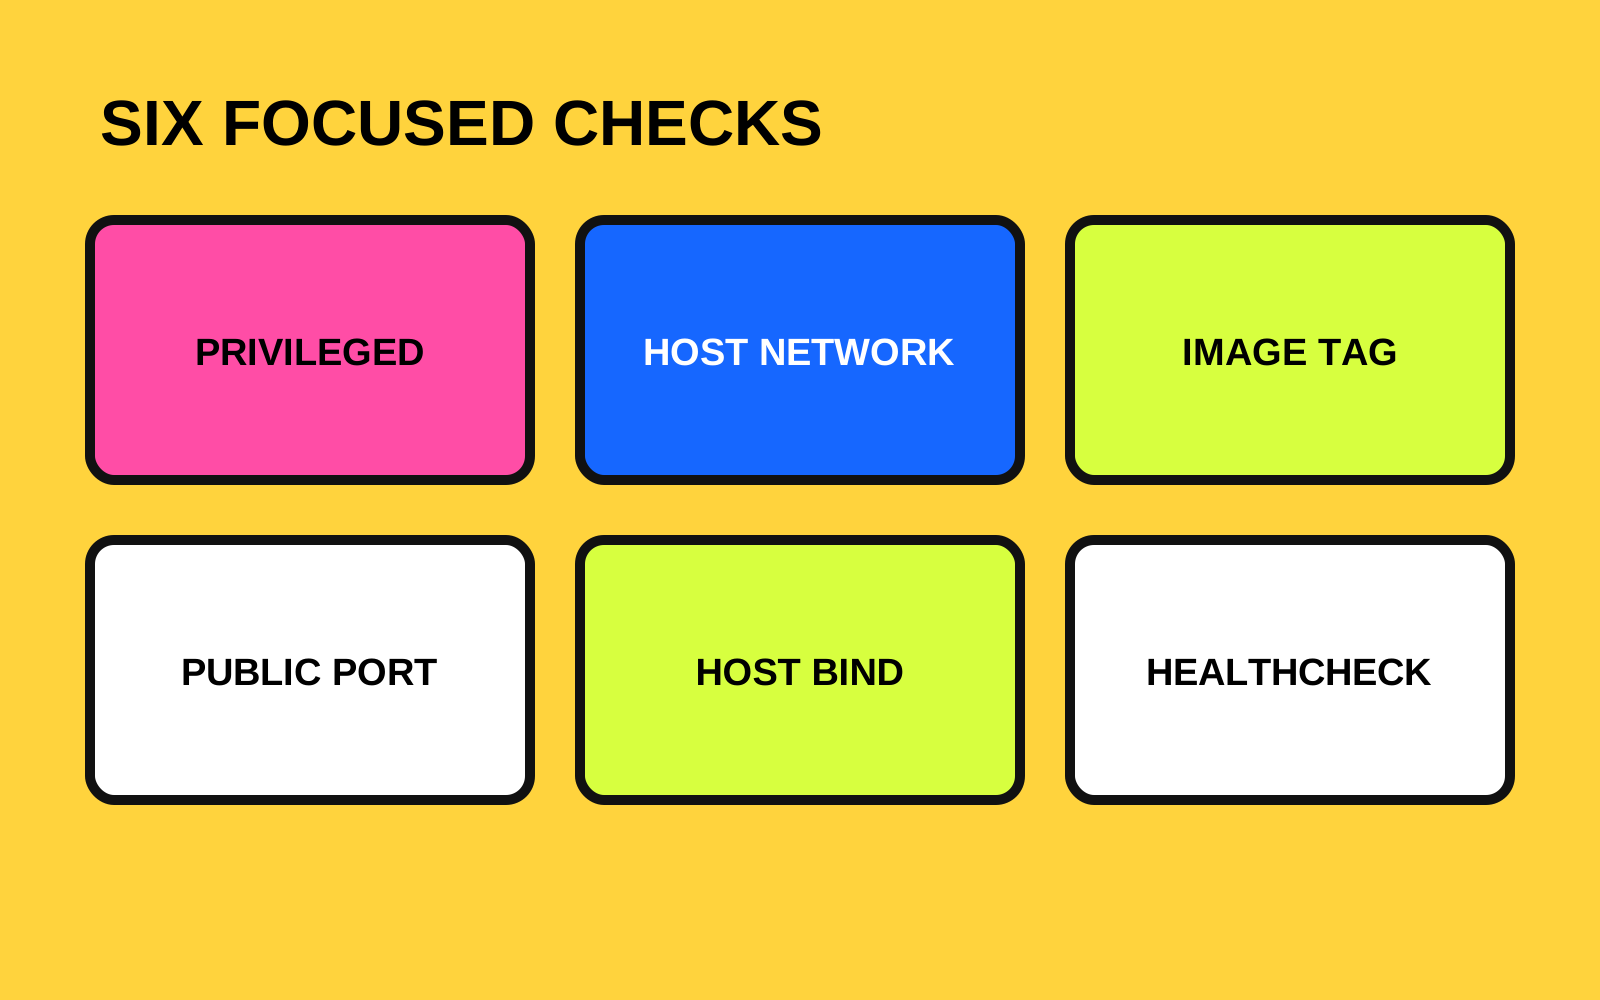
Surfaces privileged mode, host networking, unpinned images, public ports, writable host binds and absent health checks.
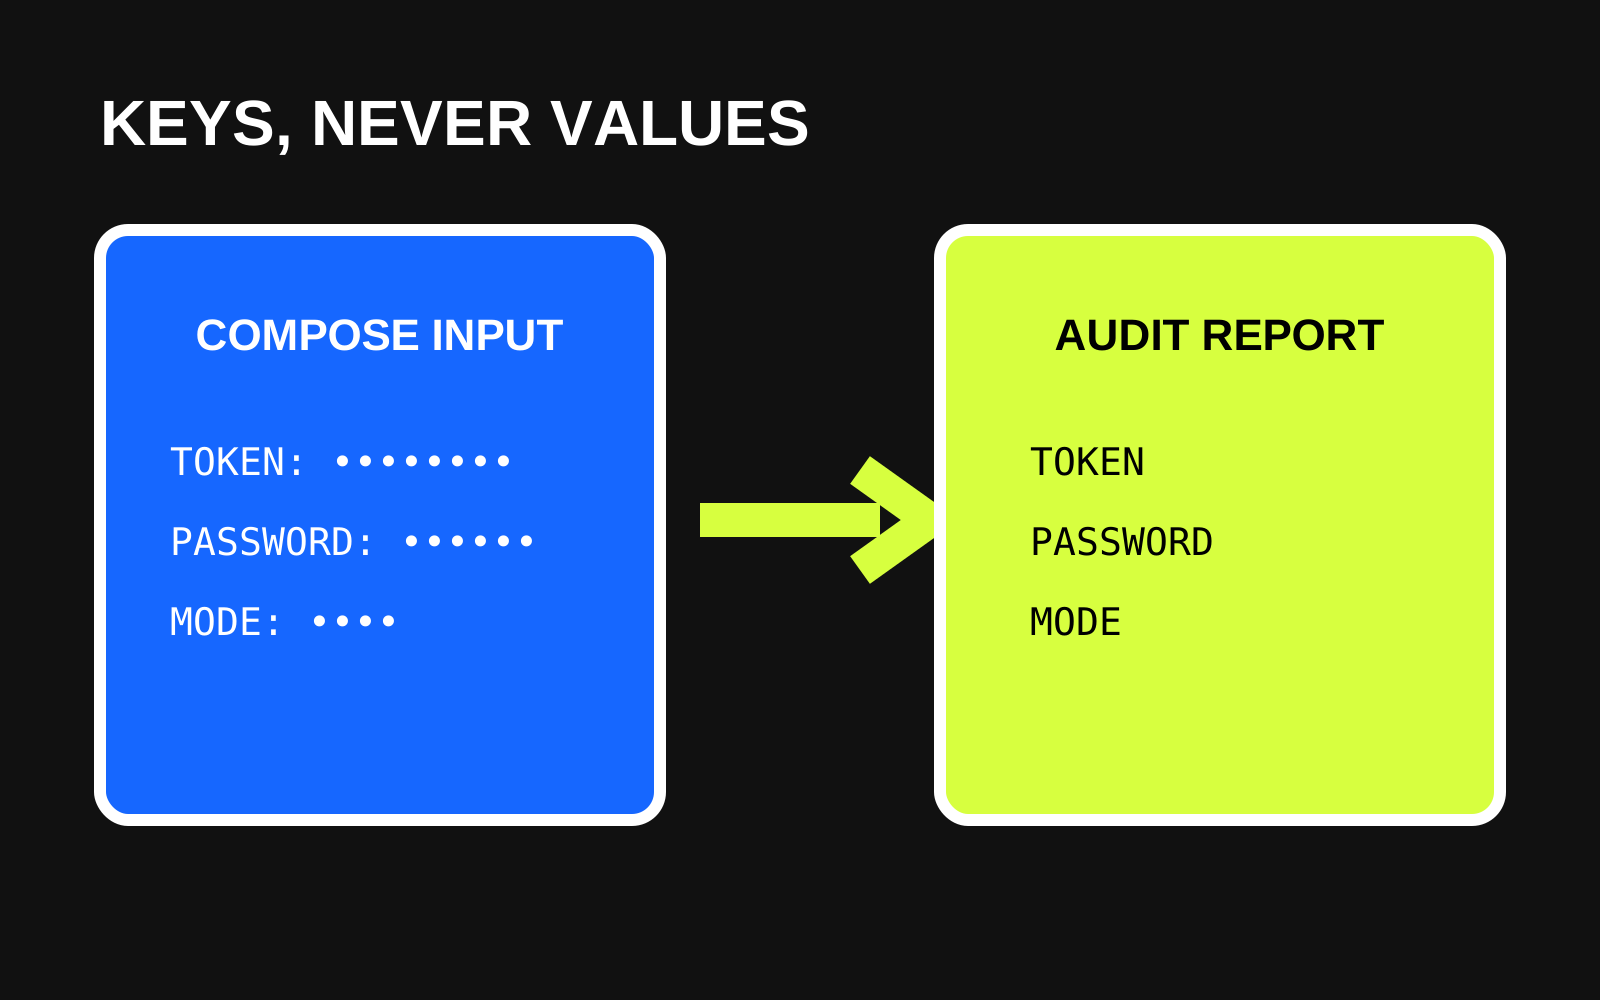
Names services, rules and safe structural evidence while listing environment keys without their configured values.
Audits one local normalized JSON document without invoking Docker or changing containers and configuration.
Six focused configuration checks
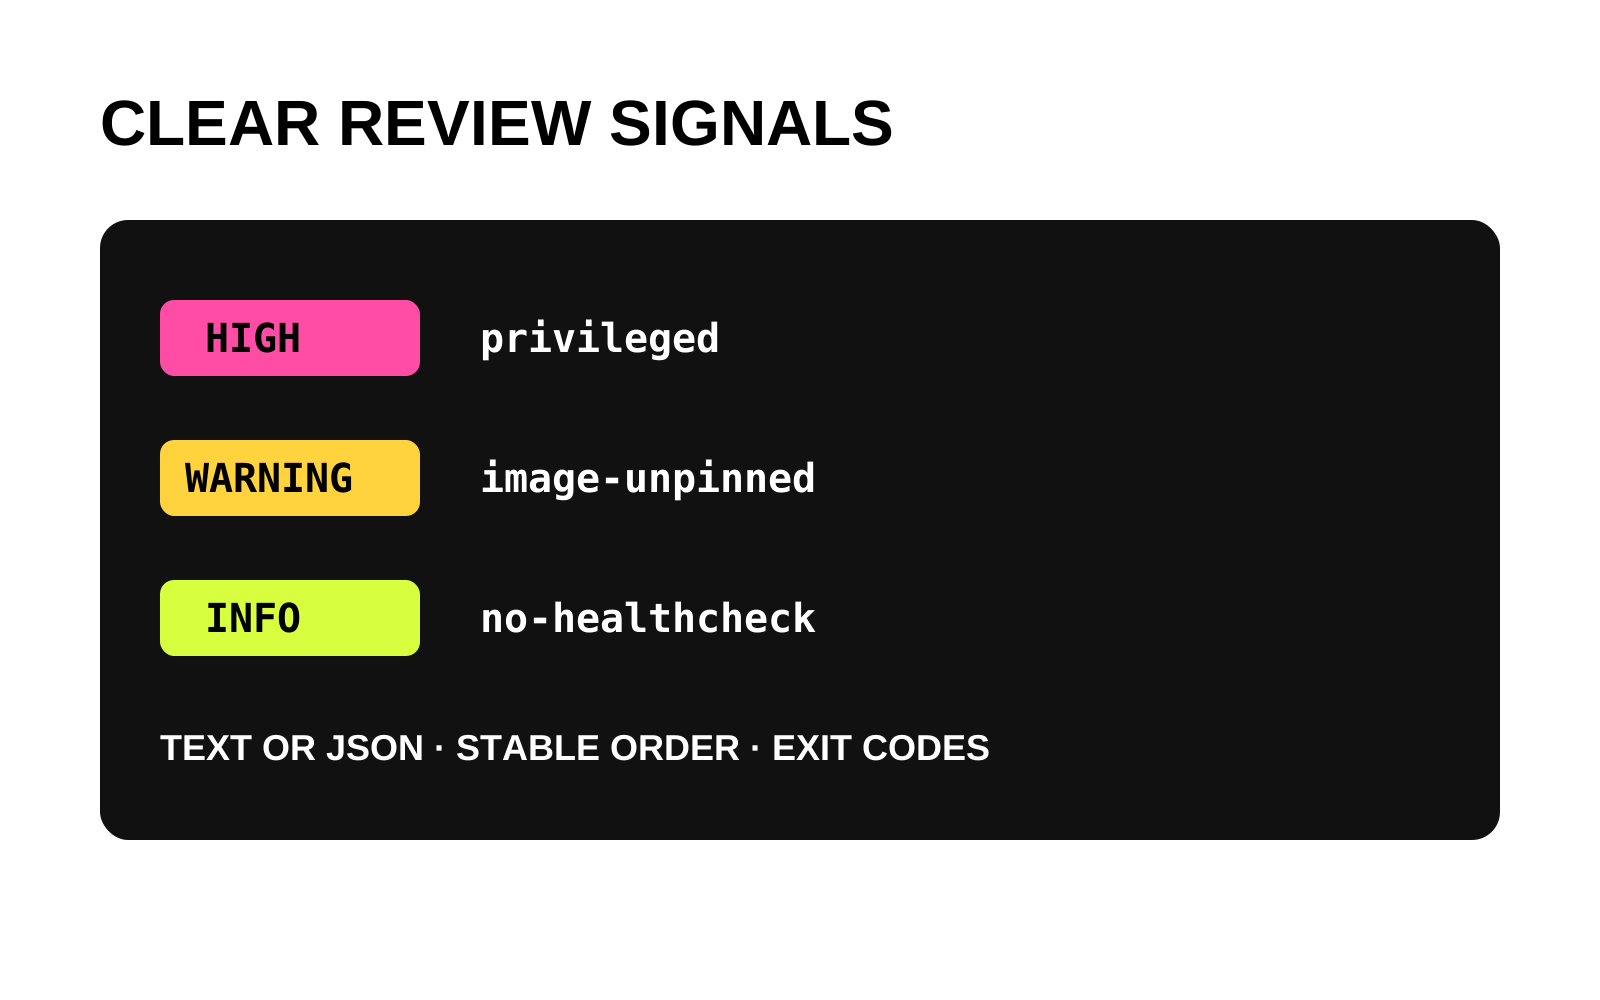
High, warning and informational severity levels
Environment values omitted
Up to 100 bounded services
Two-megabyte input boundary
Text and JSON output
Ten standard-library tests included
Argparse, pathlib, collections and JSON provide the complete dependency-free command-line workflow.
Consumes the normalized JSON shape produced by docker compose config rather than implementing an incomplete YAML parser.
Ten tests cover each focused rule, privacy boundaries, malformed and oversized inputs, deterministic output and CLI exit codes.