Local signature generation
Creates a reviewable t=timestamp,v1=signature header from exact payload bytes and a secret read from an environment variable.
Day 032 / APIs / Webhook Security
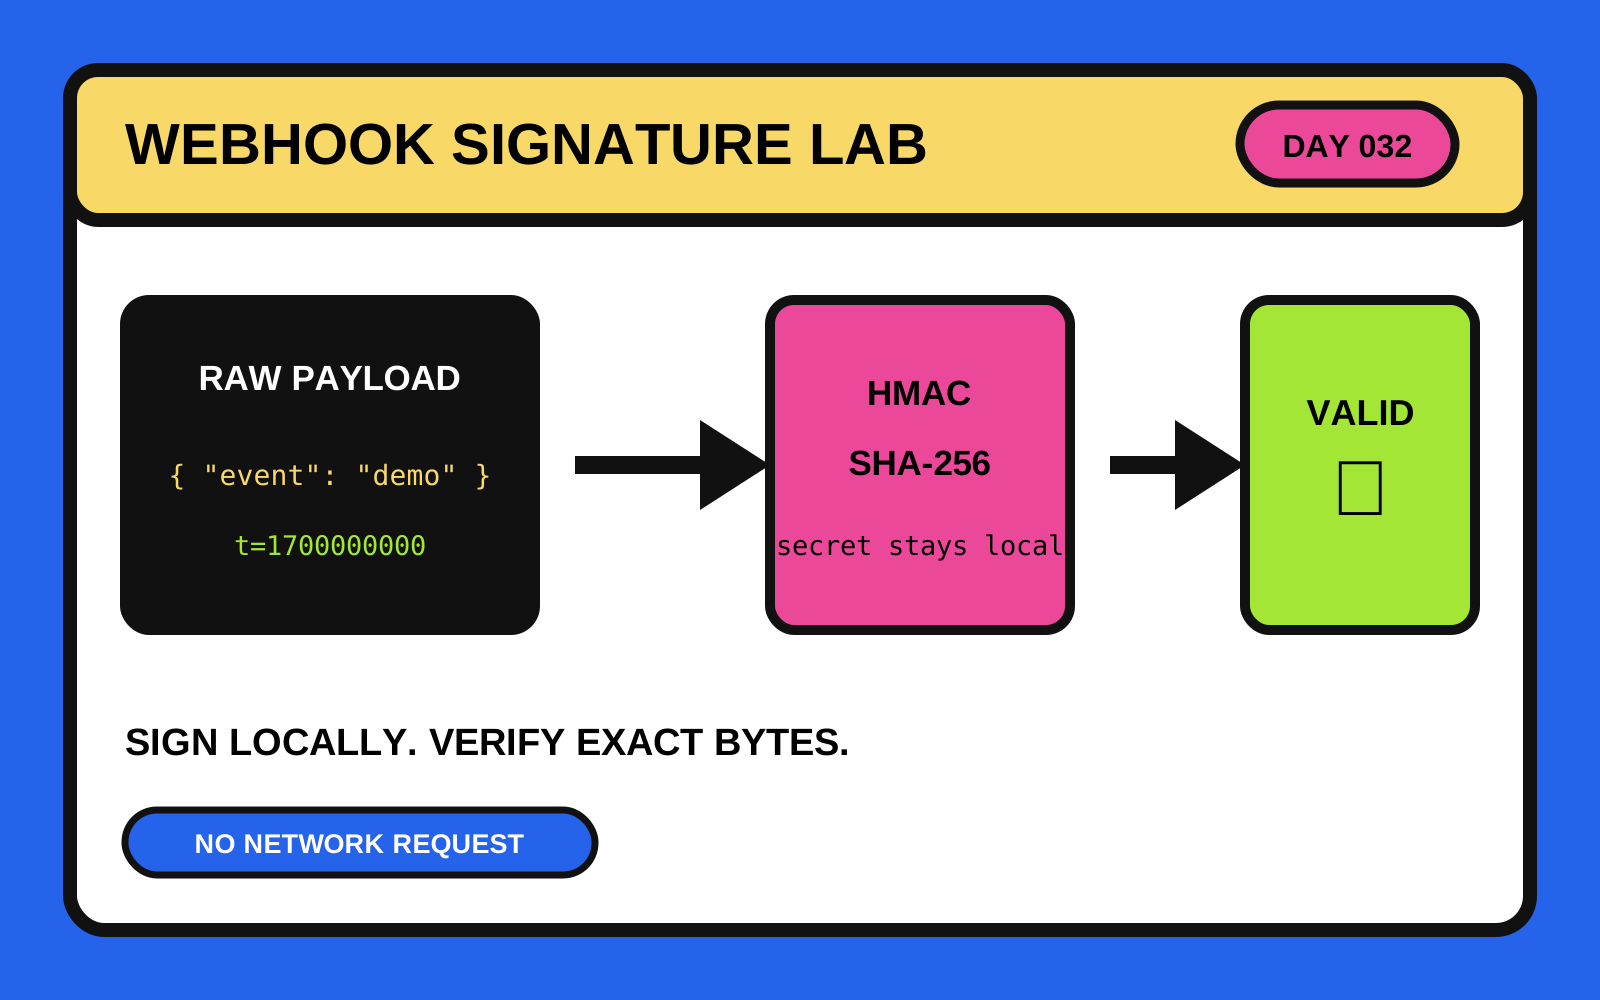
A dependency-free Python CLI for signing and verifying local webhook payloads with timestamped HMAC-SHA256, constant-time comparison and replay-age checks.
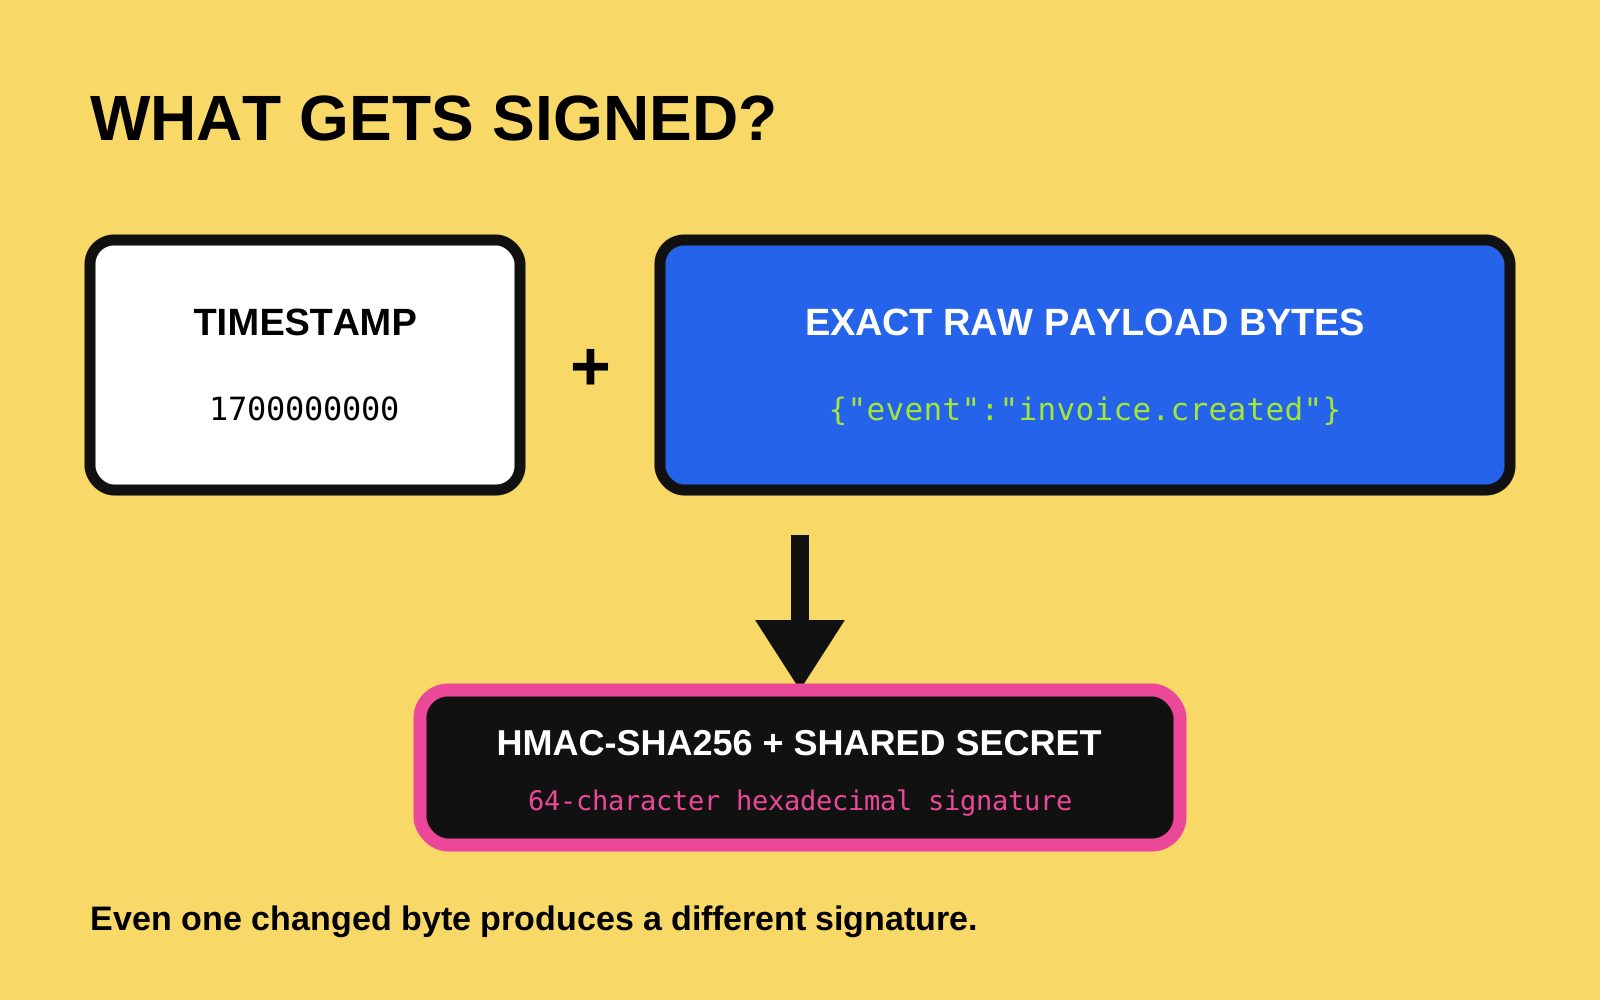
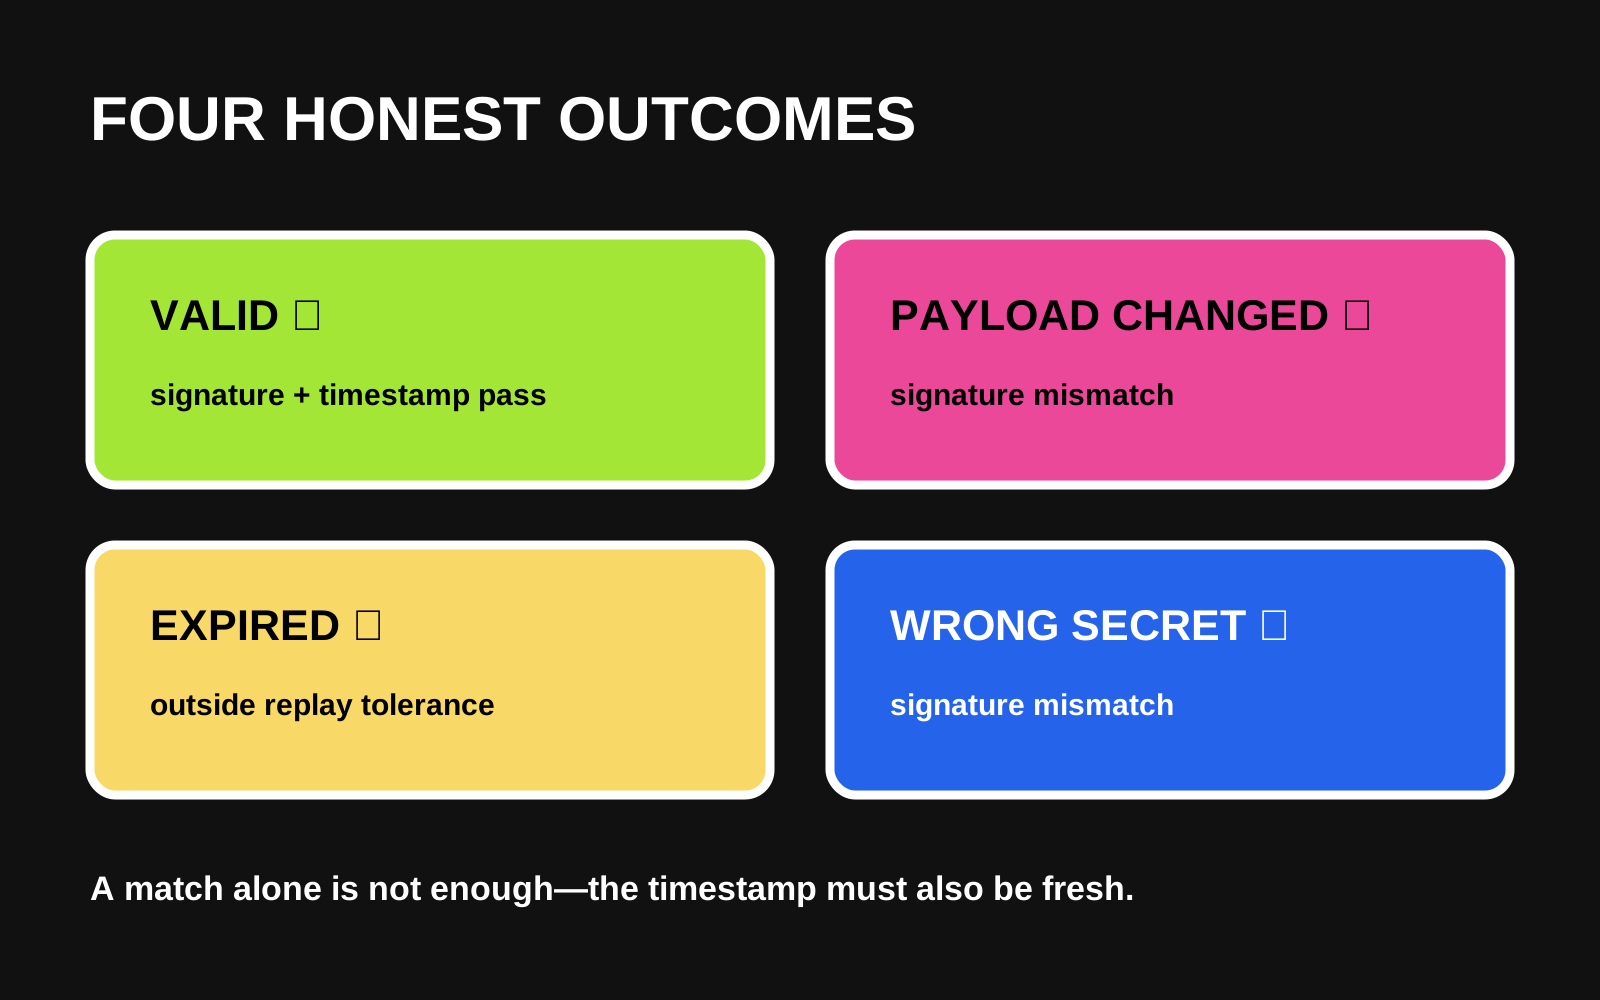
Creates a reviewable t=timestamp,v1=signature header from exact payload bytes and a secret read from an environment variable.
Separates signature matching from timestamp freshness so changed payloads, wrong secrets and expired requests remain distinct.
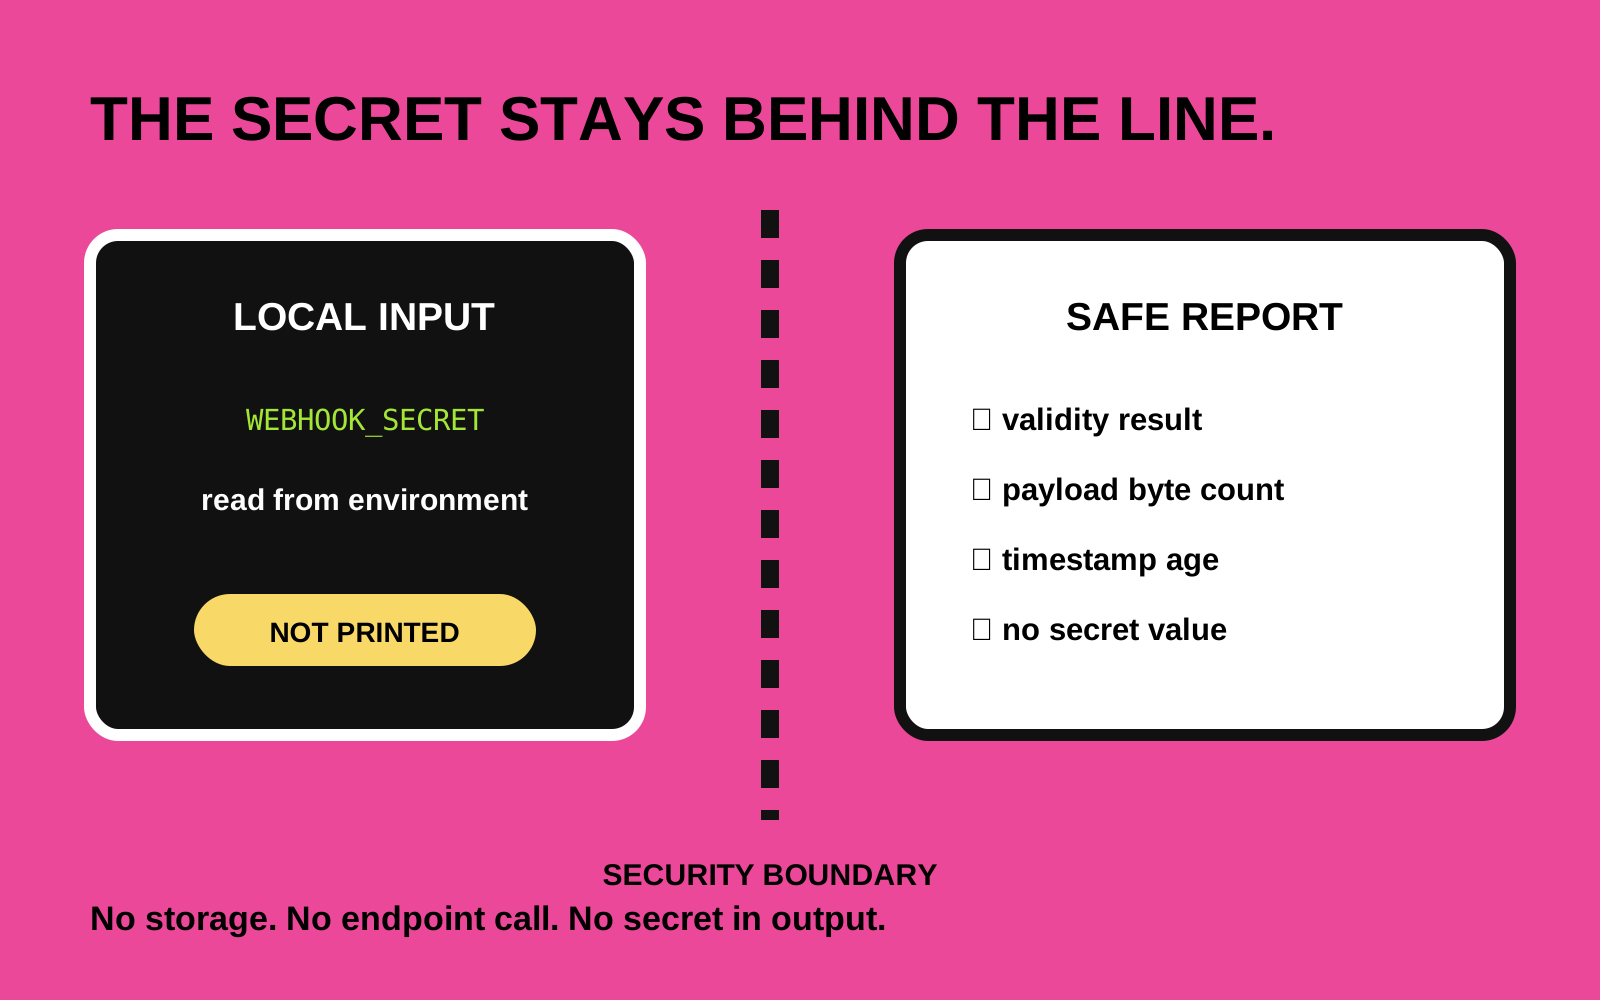
Makes no network request, stores no secret and documents that production integrations must follow each provider's exact specification.
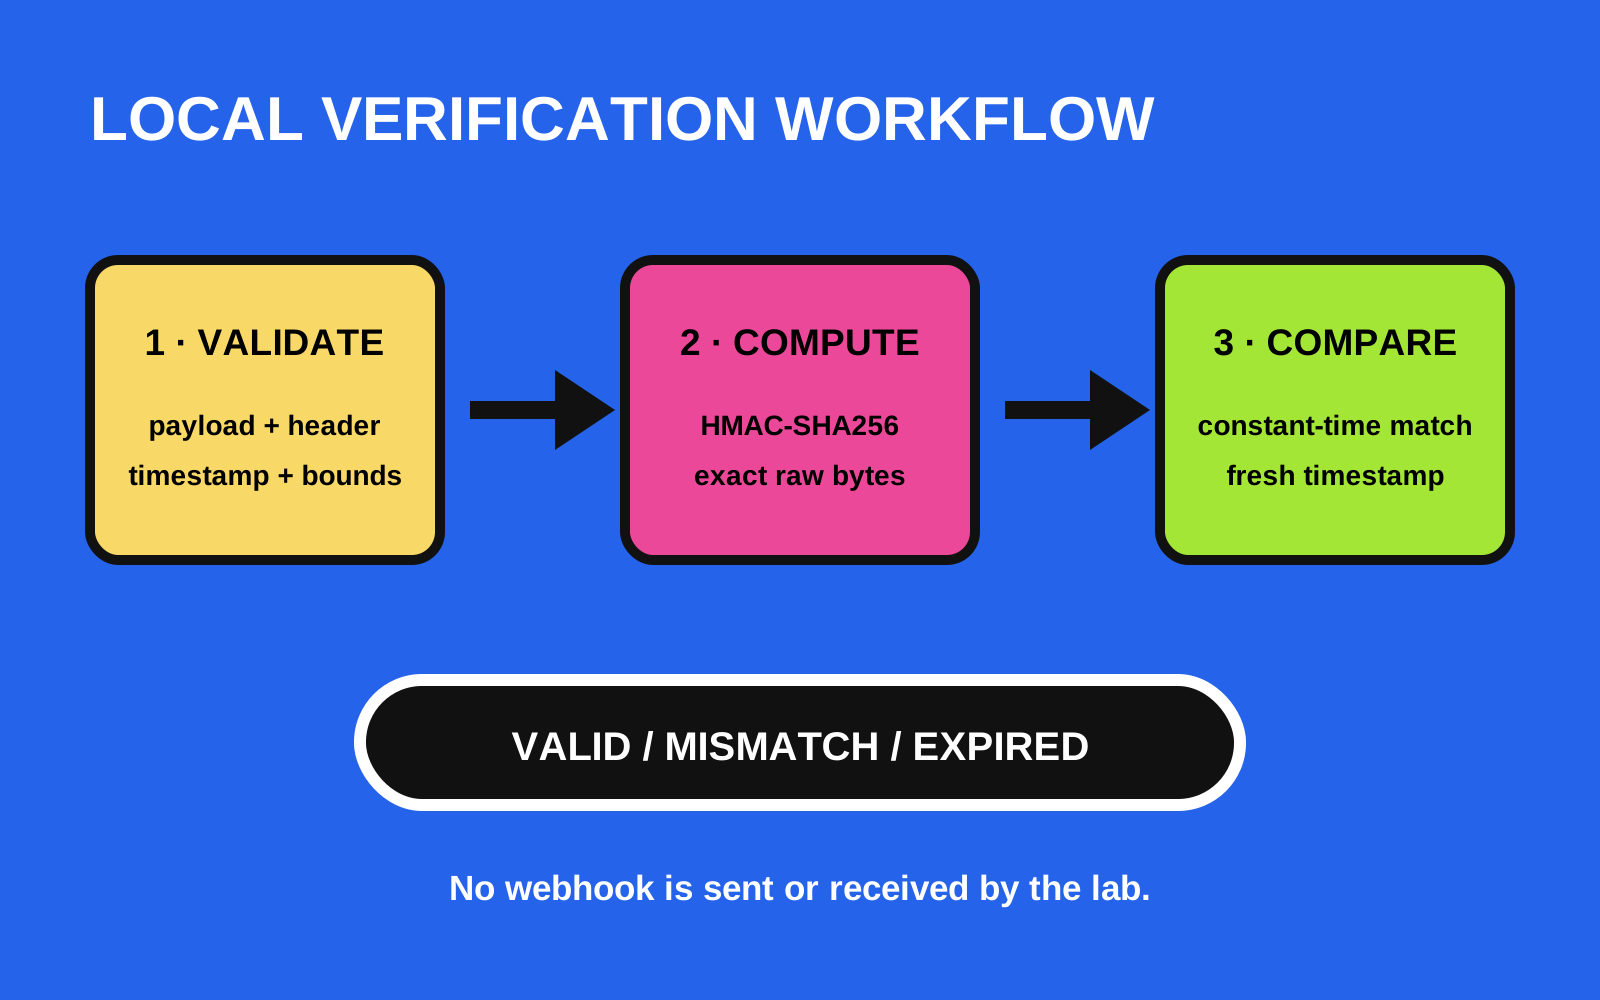
Timestamped HMAC-SHA256 signatures
Exact raw-byte verification
Constant-time comparison
Replay-age tolerance checks
Secrets omitted from every report
Twelve standard-library tests included
Hmac, hashlib, argparse, pathlib, regular expressions and JSON provide the complete dependency-free CLI.
Exercises raw-byte signing, bounded header parsing, constant-time comparison and replay-age validation.
Twelve tests cover known signatures, round trips, payload changes, wrong secrets, timestamp boundaries, multiple signatures and CLI behavior.